Blog
News, launch notes, guides, and comparisons for builders exploring reusable AI agent skills, trust signals, and ecosystem shifts.
Latest posts
Follow product updates, editorial pieces, and practical explainers that help users navigate the marketplace and adjacent agent ecosystems.
-
A Backup Restore Drill Packet for Agent-Managed Systems
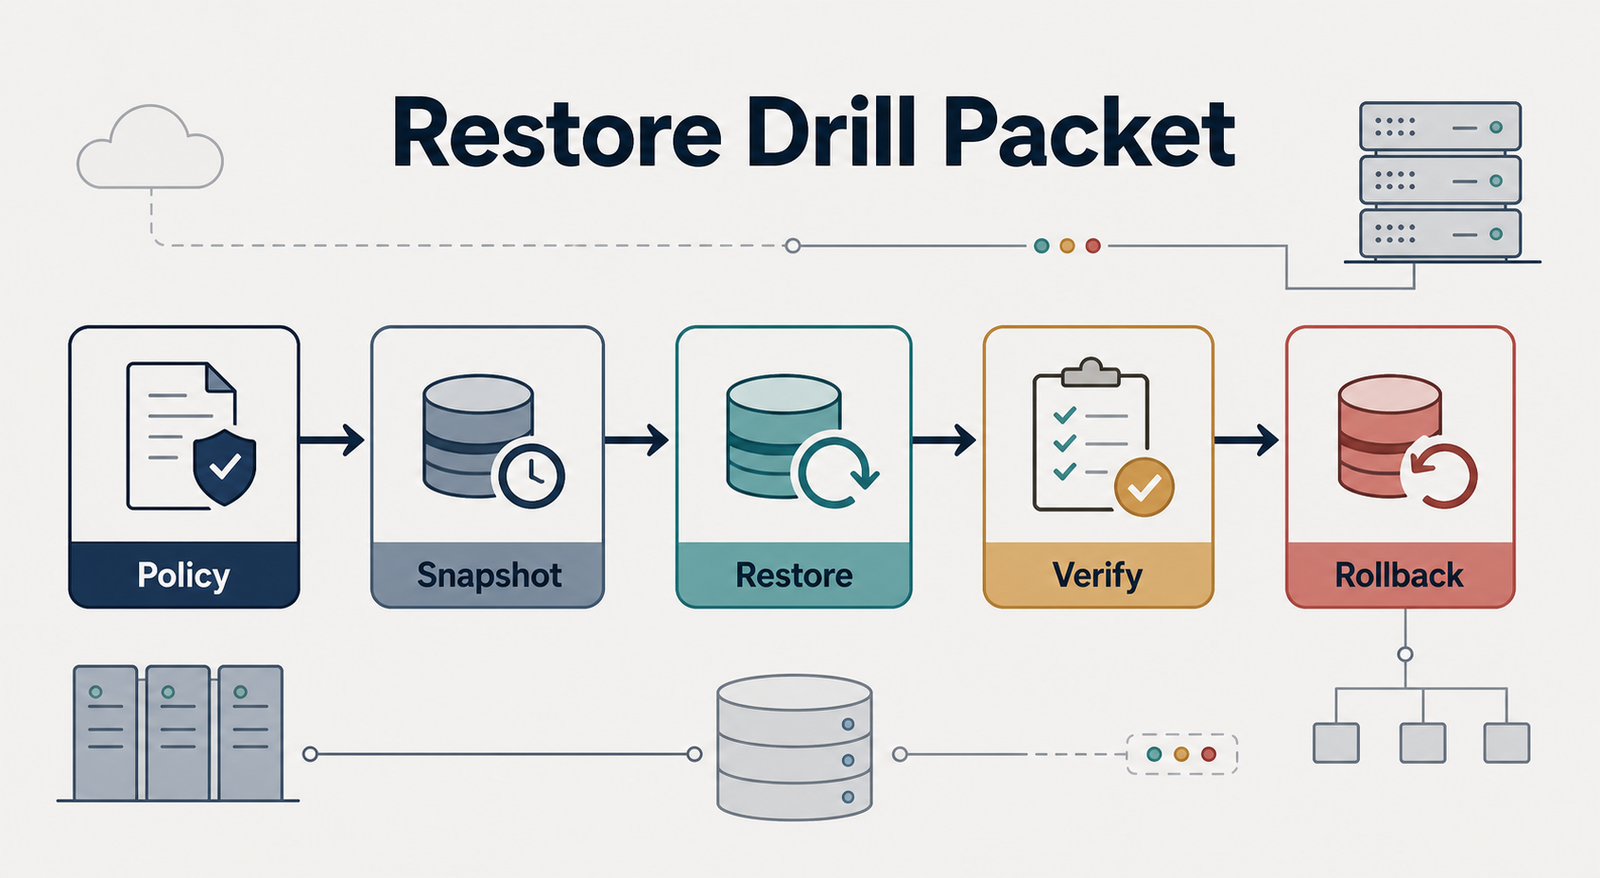
Backups are not proven when an agent finishes a scheduled run. They are proven when a small restore drill shows that the policy, snapshot, credentials, destination, and rollback notes still work under review. That distinction matters for agent-managed systems because automation can…
-
ASE Weekly Changelog: Security, Data, and Design Review Routes
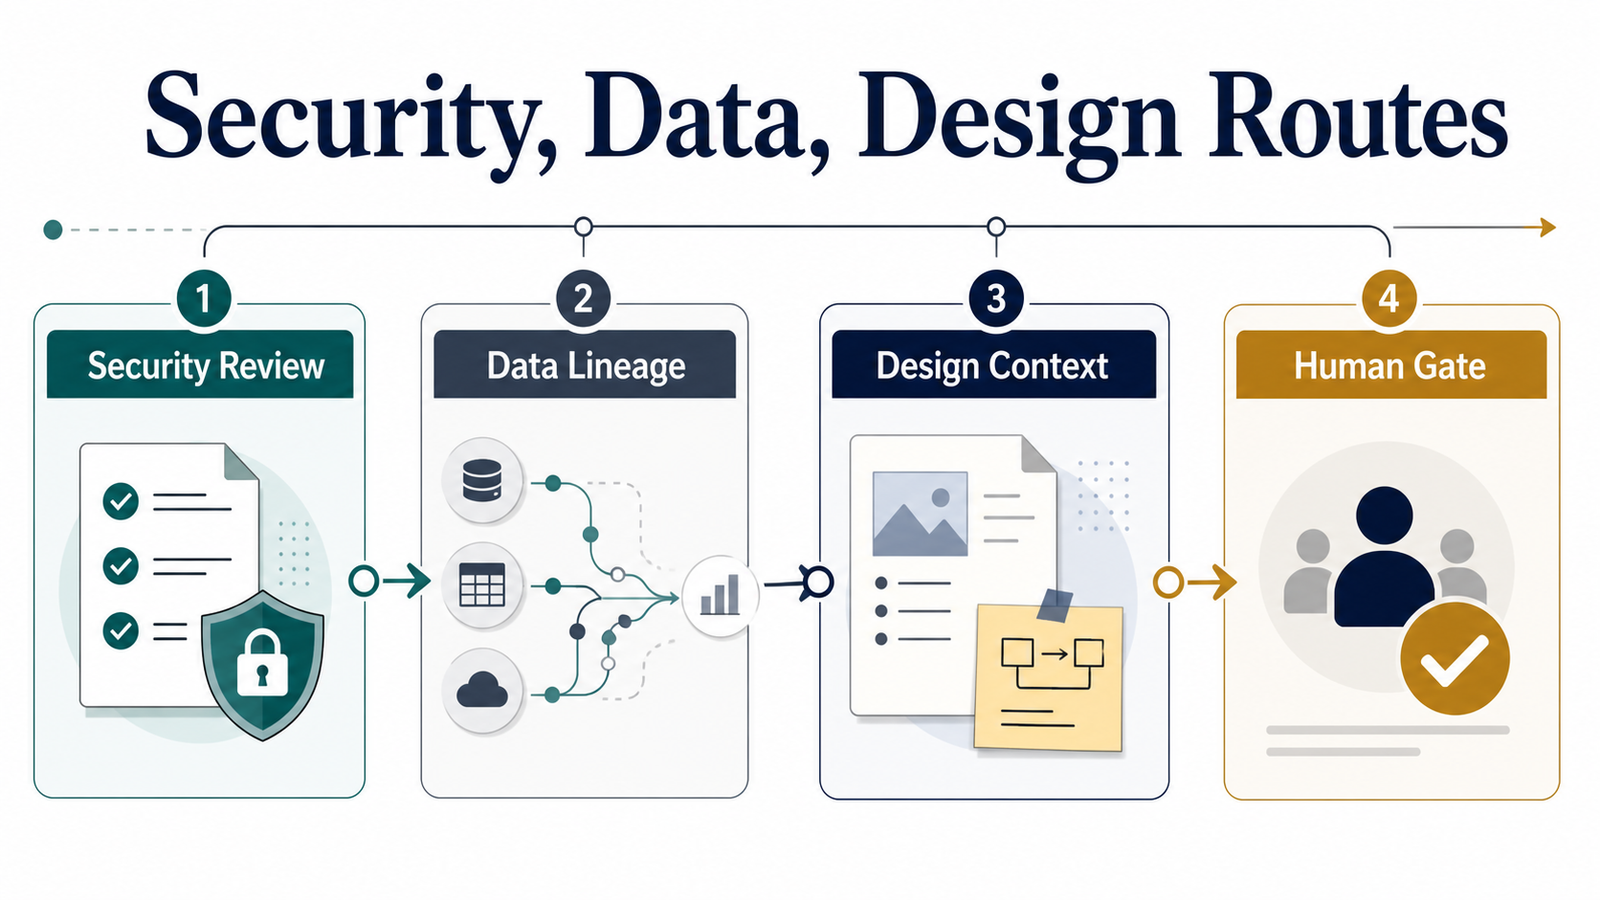
This week’s Agent Skill Exchange update is about review routes: the small, explicit paths that keep agent-assisted work from jumping straight from suggestion to production action. The useful additions sit across security, analytics engineering, and design-to-code work. Different teams will use them…
-
Figma MCP or Token Export: Choosing Design Context for Coding Agents
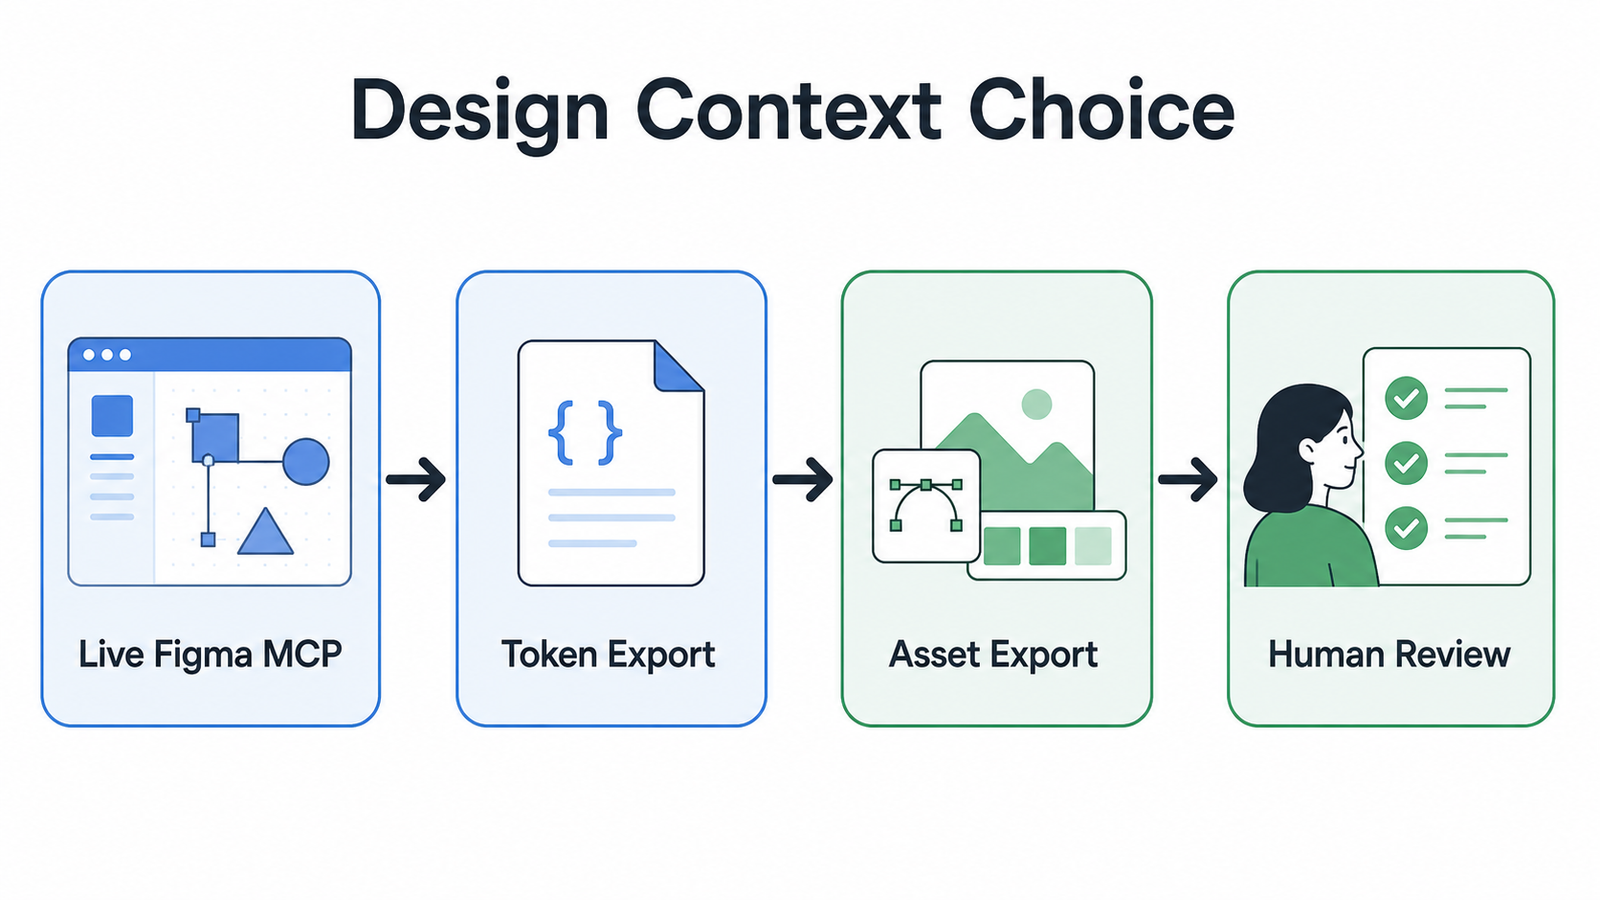
Design-to-code work gets brittle when the agent receives the wrong kind of design context. A live Figma file can answer layout questions that a token file cannot. A token export can keep a design system stable without granting an agent broad file…
-
Postgres Query Review Before Agents Touch Production Data
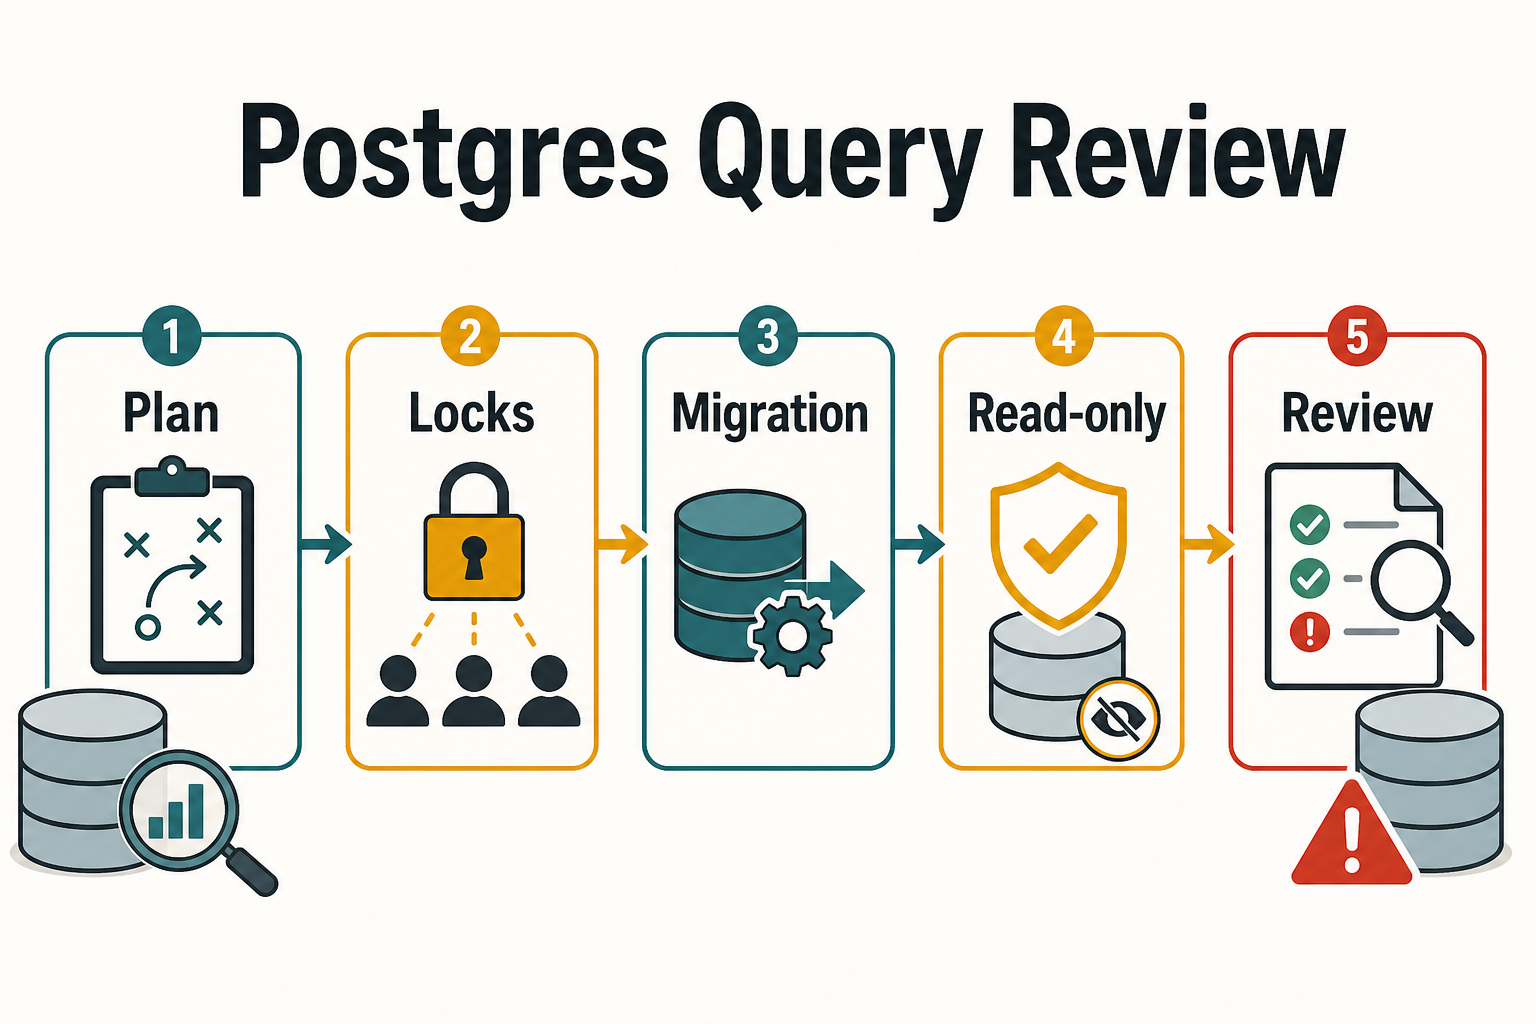
Letting an agent touch production data should start with review, not permission. A Postgres workflow needs a simple packet: what query or migration is proposed, why it is needed, what it might lock or scan, how to observe it live, and who…
-
Skill Spotlight: Slack Digest and Task Routing for Busy Teams
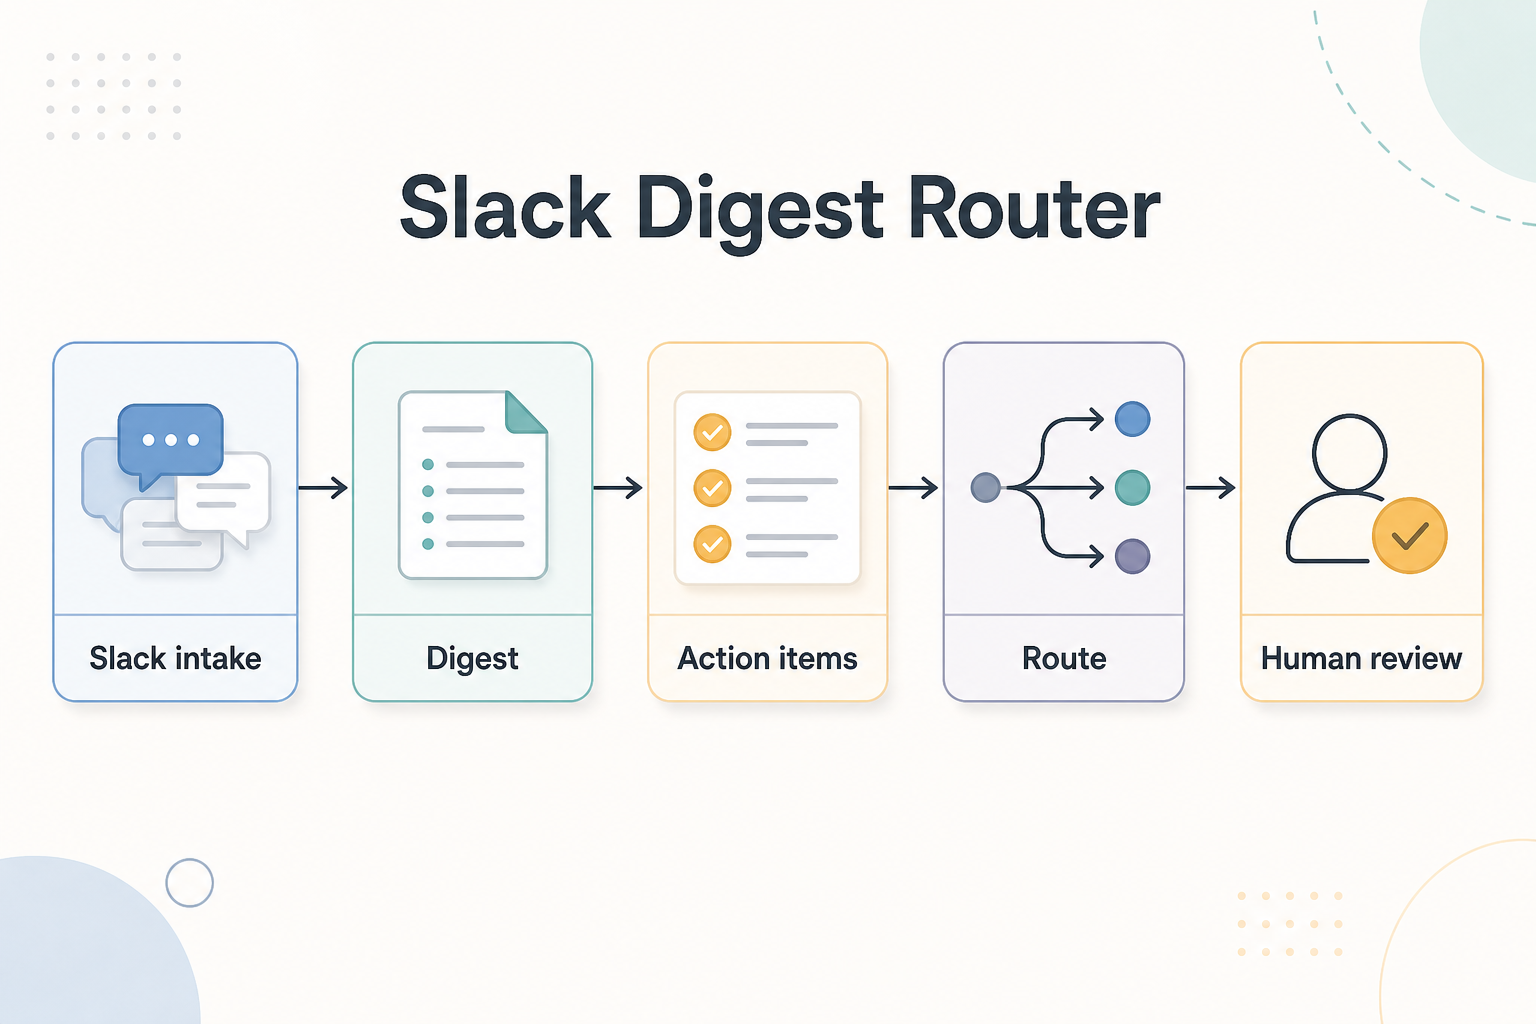
Slack is often where work first appears, but it is a poor place to let every request become an immediate interruption. A useful agent workflow treats Slack as intake: collect the right messages, summarize what changed, extract action items, and route only…
-
A Data Quality Review Stack for dbt Changes
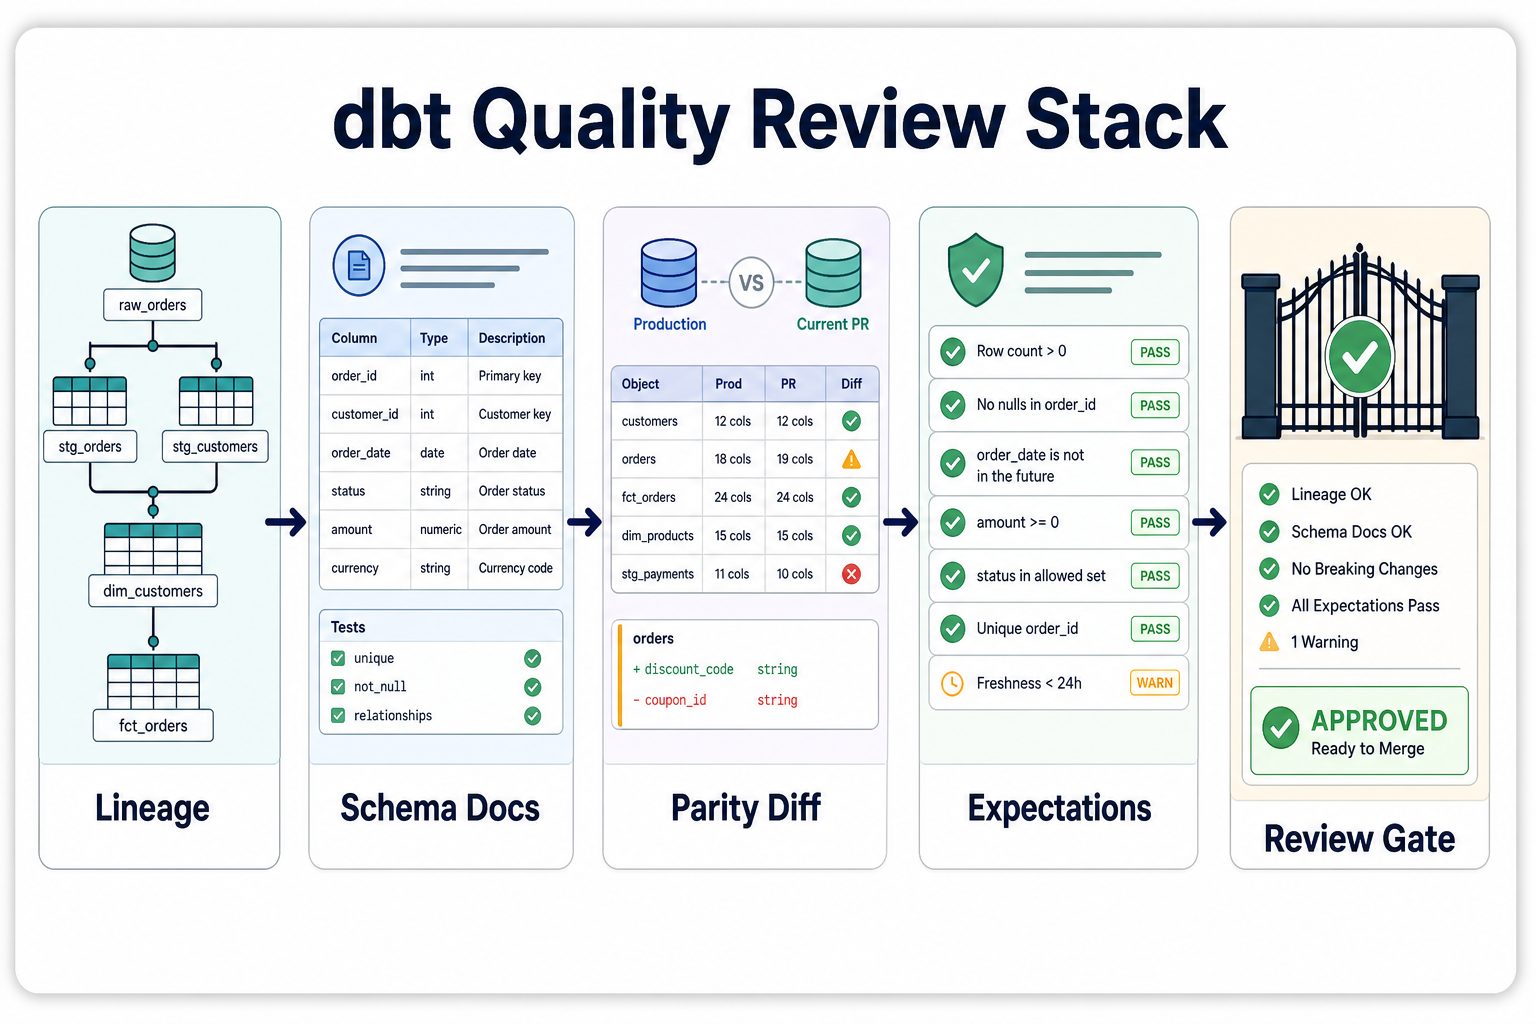
dbt changes can look clean in a pull request and still break trust in the warehouse. The risky part is rarely one SQL file by itself. It is the combination of lineage, schema metadata, model parity, expectation coverage, and the review gate…
-
Trivy, Semgrep, Checkov, or ZAP: Which Security Gate Fits the Change?
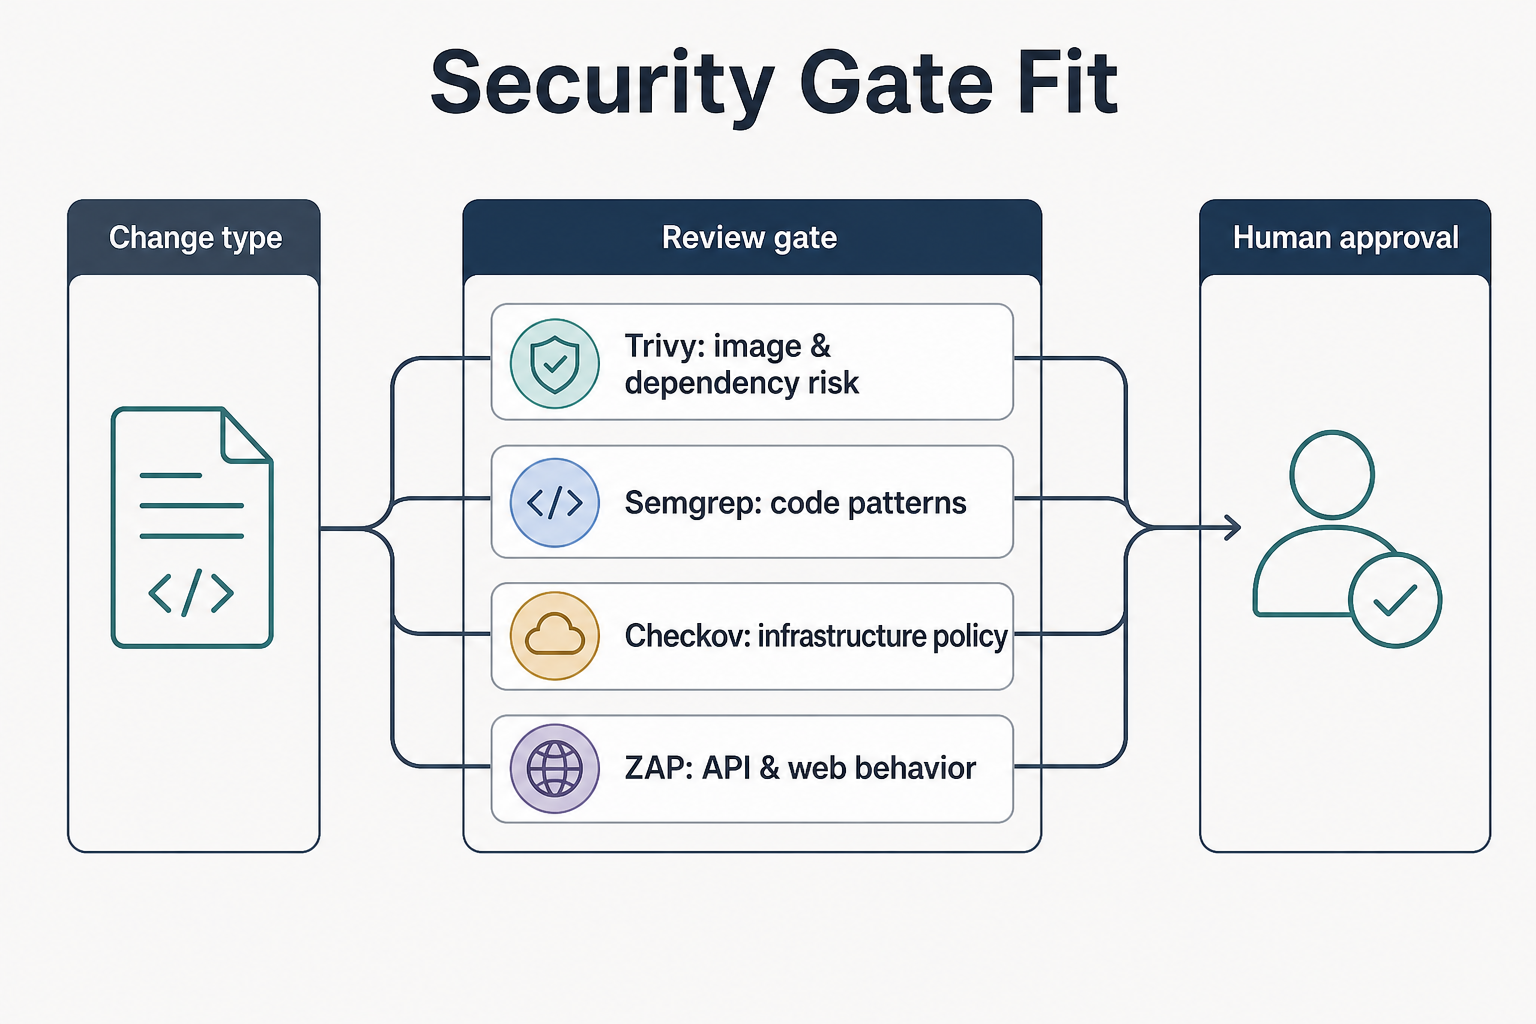
Security review gets messy when every agent-made change is pushed through the same gate. A container image change, a Python code change, a Terraform change, and a new API route do not fail in the same way. They need different evidence, and…
-
An OpenAPI Release Packet Before Agents Generate Clients
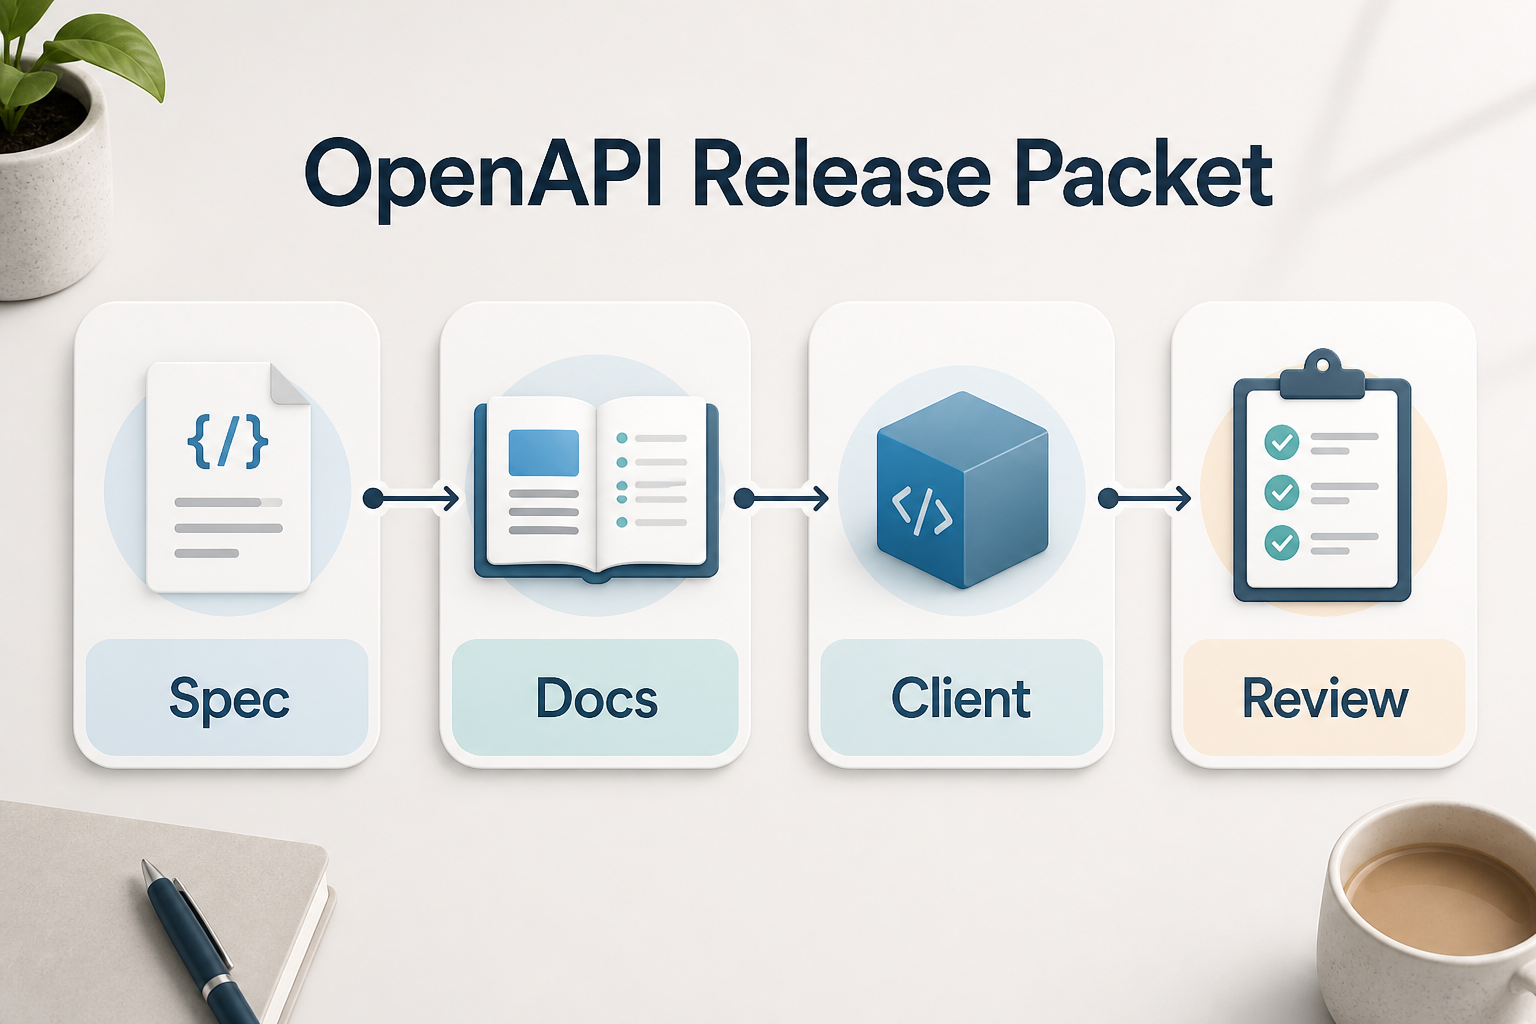
OpenAPI files are often treated as a handoff artifact: the API team updates the spec, a docs job renders reference pages, and client SDKs are regenerated somewhere nearby. That is workable when humans read every diff. It is weaker when agents start…
-
Skill Spotlight: OpenSRE for Incident Triage Evidence
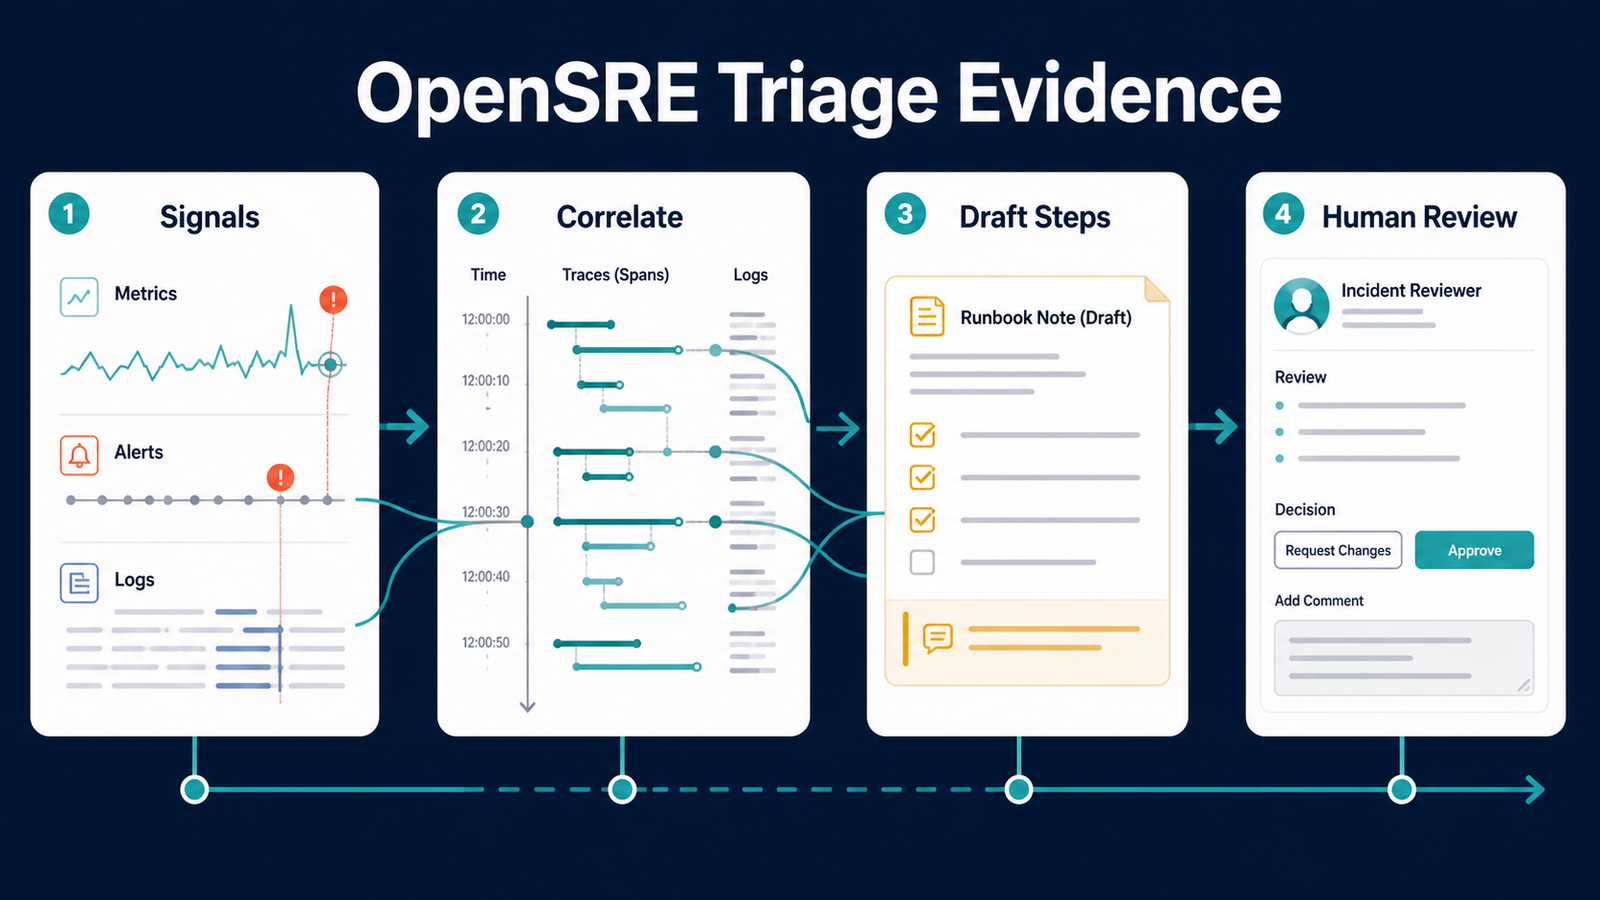
OpenSRE is useful when an incident has enough telemetry to inspect but not enough shared context for a clean first read. The right job is not to let an agent remediate production on its own. The better job is to gather evidence…
-
A Finance Ops Packet for Invoices, Sheets, and Exception Review
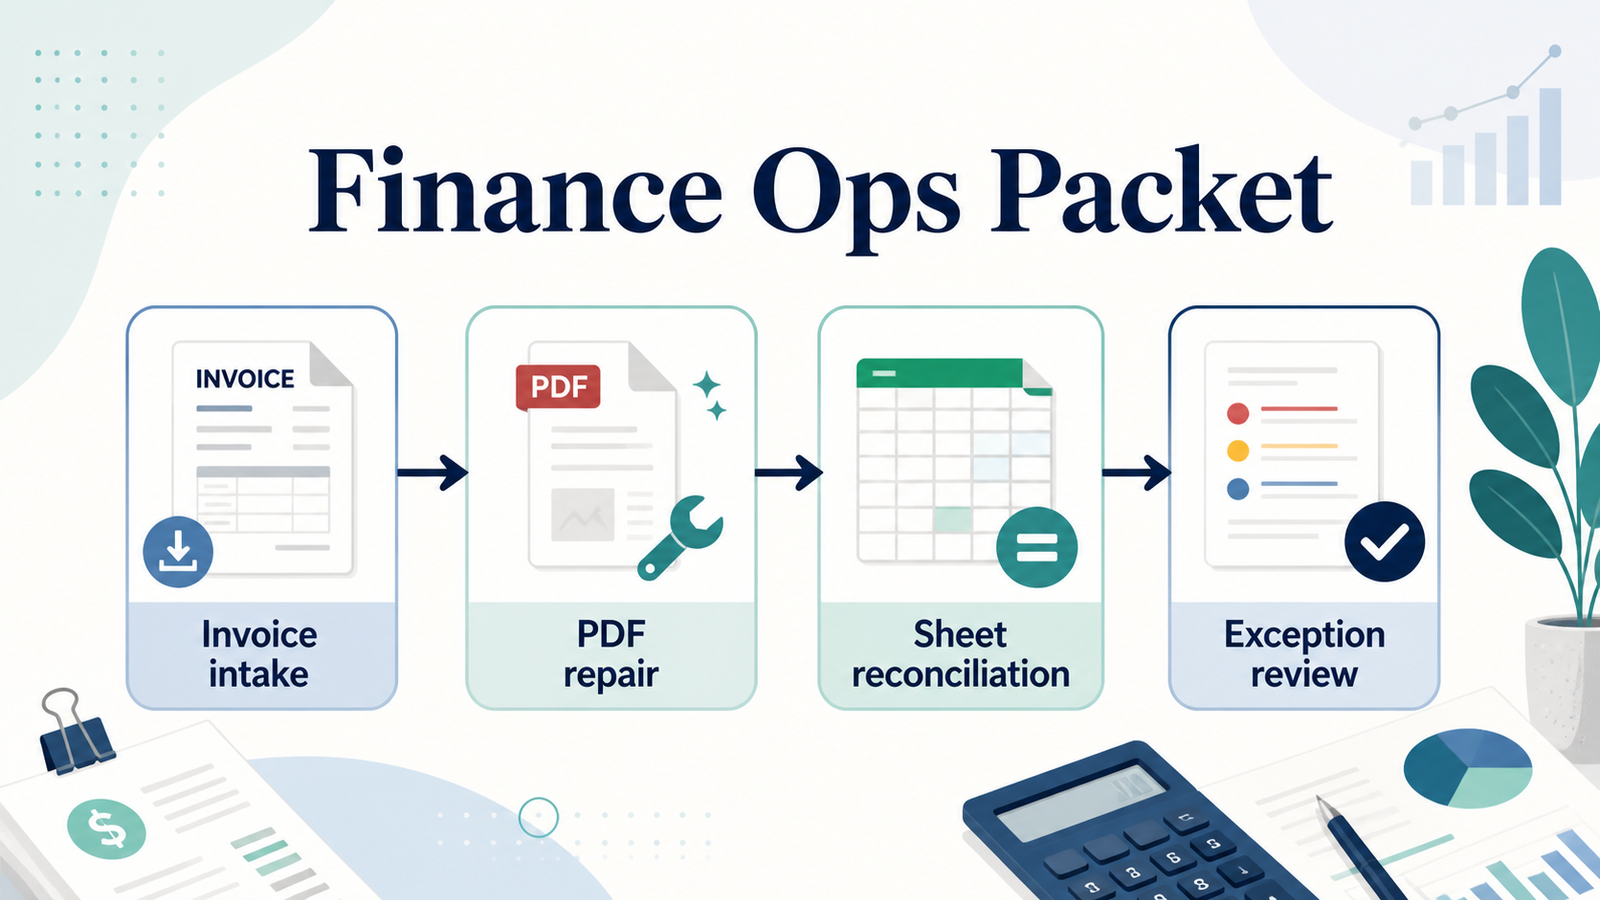
A finance ops packet is the review bundle a team can trust before an invoice is paid, corrected, disputed, or escalated. The useful version is not just extracted text from a PDF. It ties the original vendor document, any PDF repair notes…